Set up the official Google MCP servers
The official Google Drive, Google Calendar, and Gmail MCP servers give AI agents access to a user's Drive files, calendar events, and Gmail messages under that user's own Google identity. This guide covers setting the OAuth consent screen to internal use, creating an OAuth client in Google Cloud, and connecting each server to MintMCP.
MintMCP also offers a bundled Google Workspace connector that uses MintMCP's own shared OAuth apps instead of a client you create yourself: see Next steps if you want that path instead.
Prerequisites
- A MintMCP admin account
- A Google Workspace organization, since an Internal OAuth consent screen only works for a Cloud project owned by a Workspace (or Cloud Identity) organization, not a personal Google account
- A Google Cloud project with permission to enable APIs and create OAuth credentials
Enable the Google APIs
- Go to console.cloud.google.com and select or create a project owned by your Workspace organization.
- Go to APIs & Services → Library and enable the API for each server you're connecting: Google Drive API, Google Calendar API, Gmail API.
Set the OAuth consent screen to Internal
The Gmail and Calendar scopes these servers use are Google restricted and sensitive scopes. An externally published app needs a CASA security assessment to use them; an Internal user type skips it and limits sign-in to your Workspace organization.
- Go to console.cloud.google.com/auth/audience for your project.
- Set User type to Internal and fill in the required fields: App name (for example,
MintMCP Google), User support email, and Developer contact information. - Go to console.cloud.google.com/auth/scopes and click Add or remove scopes.
- Add the scopes listed under each server's tab below, then click Update and Save. Only scopes for APIs you've already enabled appear in the picker.
Create the OAuth client
The OAuth client gives MintMCP a Client ID and secret to broker each user's Google sign-in. Create one Web application client and point its redirect URI at MintMCP's callback. All three servers can share this same client.
-
Go to console.cloud.google.com/auth/clients and click Create client.
-
Set Application type to Web application and give it a name (for example,
MintMCP Google). The name only identifies the client in the console.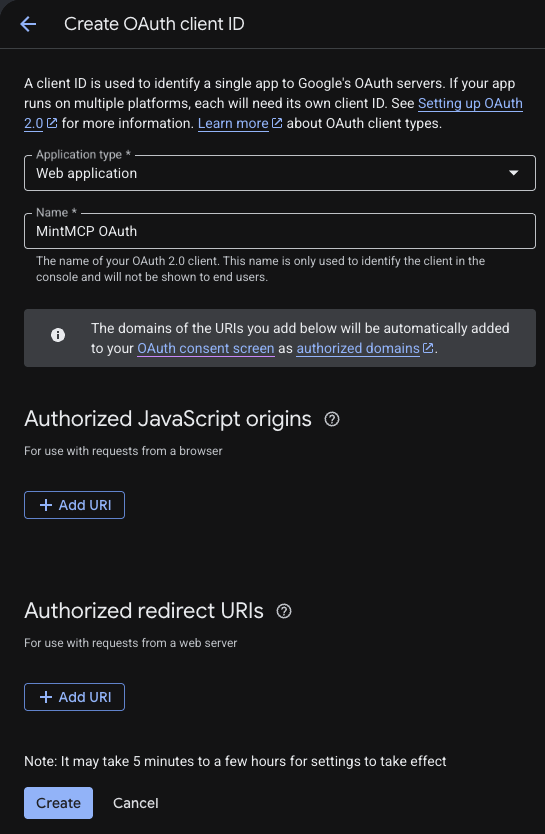
-
Under Authorized redirect URIs, click Add URI and enter MintMCP's callback URL:
https://app.mintmcp.com/oauth/callback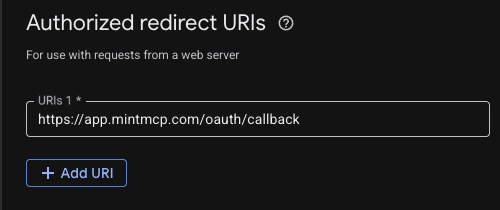
-
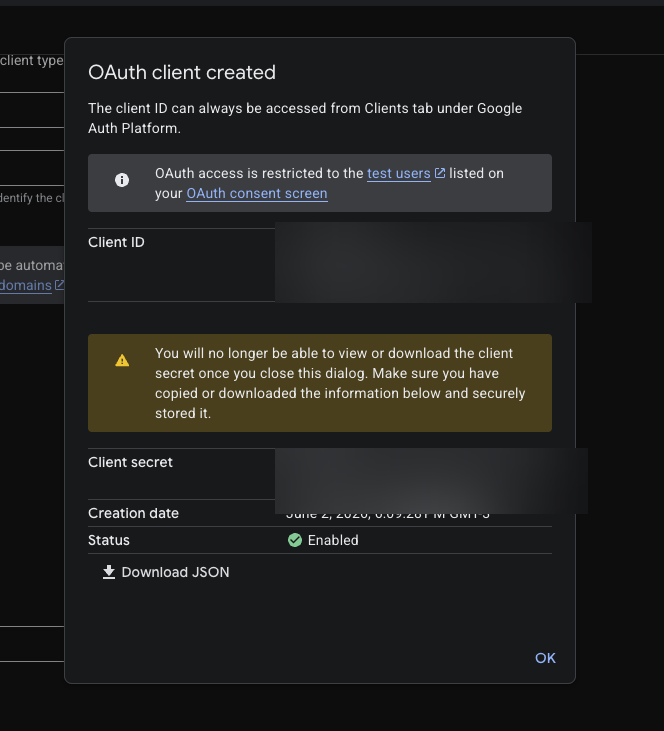
Click Create. Google shows the Client ID and Client secret once; copy both now because you can't view the secret again after closing the dialog.
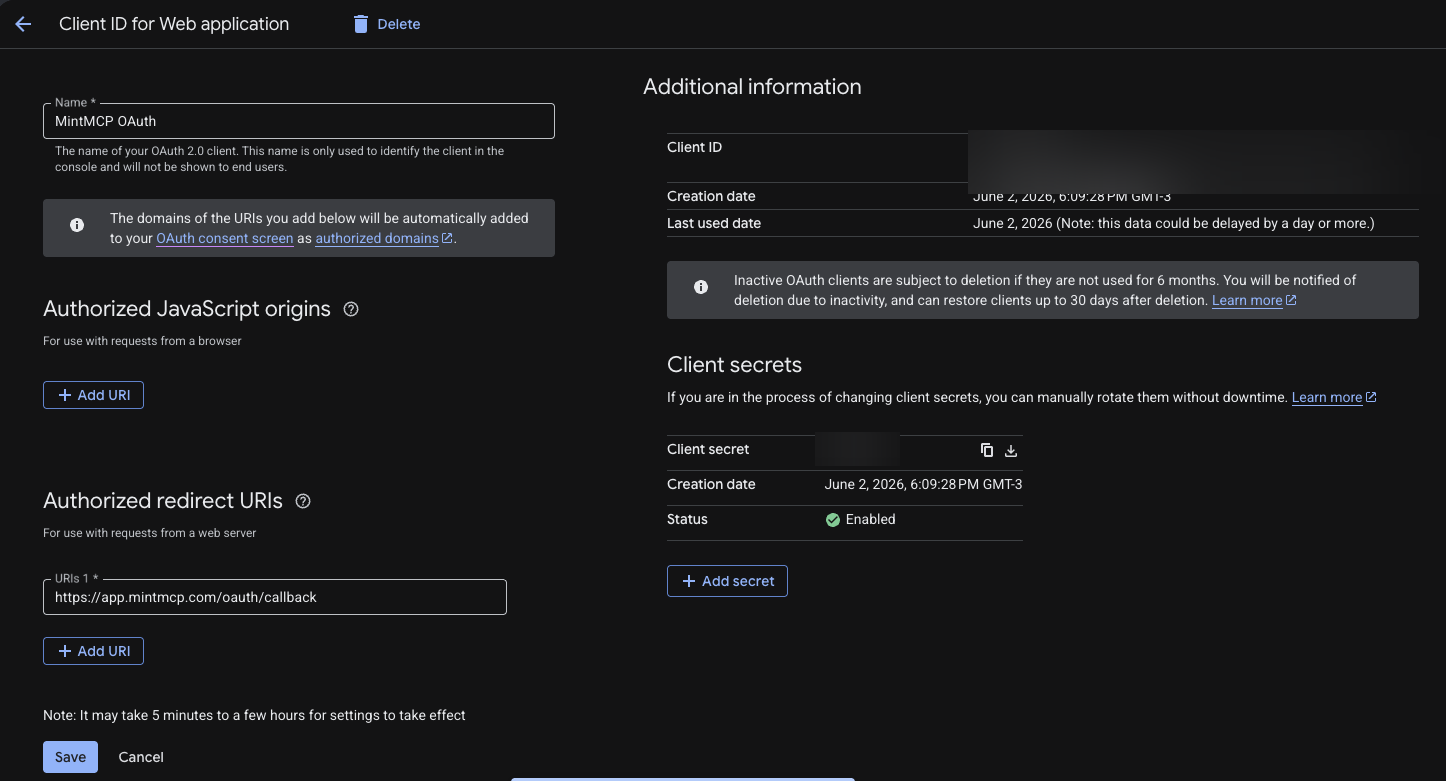
Reopen the client anytime from the Clients list to edit its redirect URIs or rotate the secret.
Add the servers to MintMCP
Each server is a separate connector, marked Recommended, in the MintMCP store. Install the ones your organization needs and paste the same Client ID and Client Secret into each.
- Google Drive
- Google Calendar
- Gmail
- In MintMCP, go to MCP store → Manage store.
- Find the Google Drive connector, marked Recommended, and click to install it.
- Enter the Client ID and Client Secret from the OAuth client you created.
- Click Install.
Add these scopes to the OAuth consent screen's Data Access page:
| Scope | Access granted |
|---|---|
openid | OpenID Connect authentication |
.../userinfo.email | View user email address |
.../drive.readonly | Search and read Drive files |
.../drive.file | View and manage files created or opened with this app |
- In MintMCP, go to MCP store → Manage store.
- Find the Google Calendar connector, marked Recommended, and click to install it.
- Enter the Client ID and Client Secret from the OAuth client you created.
- Click Install.
Add these scopes to the OAuth consent screen's Data Access page:
| Scope | Access granted |
|---|---|
openid | OpenID Connect authentication |
.../userinfo.email | View user email address |
.../calendar.readonly | List calendars and read events |
.../calendar.events.readonly | Read events on calendars the user can access |
.../calendar | Full access: create, update, and delete calendars and events |
- In MintMCP, go to MCP store → Manage store.
- Find the Gmail connector, marked Recommended, and click to install it.
- Enter the Client ID and Client Secret from the OAuth client you created.
- Click Install.
Add these scopes to the OAuth consent screen's Data Access page:
| Scope | Access granted |
|---|---|
openid | OpenID Connect authentication |
.../userinfo.email | View user email address |
.../gmail.readonly | Read emails, attachments, and labels |
.../gmail.compose | Create drafts and send email |
.../gmail.modify | Read, send, and manage labels on email (excludes permanent deletion) |
All scopes above use the https://www.googleapis.com/auth/ prefix.
The first time a user calls a tool on a given server, MintMCP directs them to sign in with Google and consent to that server's scopes. MintMCP stores and refreshes their token automatically on every subsequent call.
Security considerations
- Each user authenticates individually through OAuth, so tool calls run under that user's own Drive, Calendar, or Gmail access.
- The
gmail.modifyandcalendarscopes grant write access: email sending and label changes, and calendar and event creation, updates, and deletion. Install only the servers your organization needs. - The Internal user type restricts sign-in to accounts in your Workspace organization and skips Google's restricted-scope verification review.
- Keep the client secret secure: anyone with it can impersonate the app and request access to users' Drive, Calendar, or Gmail data.
Troubleshooting
- Sign-in fails with
redirect_uri_mismatch. The redirect URI on the Google Cloud OAuth client doesn't match MintMCP's callback. Open the OAuth client, confirm Authorized redirect URIs containshttps://app.mintmcp.com/oauth/callbackexactly, and save. Changes can take a few minutes to take effect. - Sign-in fails or the account can't complete consent. The Google account isn't a member of the Workspace organization that owns the Cloud project, since an Internal OAuth client only accepts sign-in from accounts in the same organization.
- A scope doesn't appear in the Data Access picker. The API that owns that scope isn't enabled yet. Enable the matching API (Drive, Calendar, or Gmail) in APIs & Services → Library, then try adding the scope again.
Next steps
- Google Workspace bundle: connect Drive, Gmail, Calendar, Docs, Sheets, and Slides using MintMCP's own shared OAuth apps instead of one you create
- Tool customization: control which tools are exposed to users
- MCP gateway administration: manage access and permissions